Installing And Configuring Windows Server 2012 1st Edition Pdf Download
Valid lxx-410 Dumps shared by PassLeader for Helping Passing 70-410 Exam! PassLeader now offer the newest 70-410 VCE dumps and seventy-410 PDF dumps, the PassLeader 70-410 exam questions accept been updated and ANSWERS have been corrected, become the newest PassLeader 70-410 dumps with VCE and PDF hither: http://www.passleader.com/70-410.html (512 Q&As Dumps –> 528 Q&Every bit Dumps)
BTW, DOWNLOAD part of PassLeader seventy-410 dumps from Cloud Storage: https://drive.google.com/open up?id=0B-ob6L_QjGLpfnJzOE1fWnlJOWVtaE93SnJNT3gtaTNYYnVpZkw5THBSMWRKbFlfaXh1azg
QUESTION 161
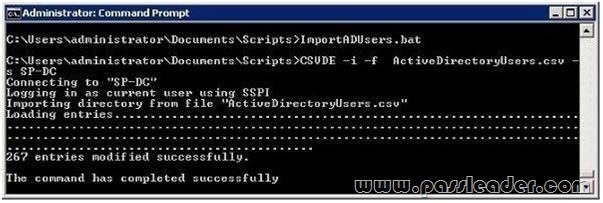
Your network contains an Active Directory domain named contoso.com. Your company hires 500 temporary employees for the summer. The human resource department gives you lot a Microsoft Excel document that contains a listing of the temporary employees. You demand to automate the creation of user accounts for the 500 temporary employees. Which tool should you employ?
A. The Add together-Fellow member cmdlet
B. ADSI Edit
C. The csvde.exe control
D. Active Directory Users and Computers
Answer: C
Explanation:
Csvde.exe is the best option to add multiple users. As you only need to export the excel spreadsheet as a csv file and make certain the parameters are right. You lot can use Csvde to import and consign Active Directory data that uses the comma-separated value format. Use a spreadsheet program such as Microsoft Excel to open this .csv file and view the header and value information.
http://support.microsoft.com/kb/327620/en-us
QUESTION 162
Your network contains 2 subnets. The subnets are configured as shown in the following table.

You lot accept a server named Server2 that runs Windows Server 2012 R2. Server2 is continued to LAN1. You run the road print command as shown in the exhibit. (Click the Exhibit push button.)

You need to ensure that Server2 can communicate with the client computers on LAN2. What should you lot do?
A. Change the metric of the 10.x.1.0 road.
B. Ready the state of the Teredo interface to disable.
C. Fix the land of the Microsoft ISATAP Adapter #2 interface to disable.
D. Run route delete 172.23.2.0.
Answer: D
Explanation:
Route is used to view and modify the IP routing table. Route Print displays a list of current routes that the host knows. Default gateways are of import to make IP routing piece of work efficiently. TCP/IP hosts rely on default gateways for virtually of their advice needs with hosts on remote network segments. In this style, individual hosts are freed of the burden of having to maintain extensive and continuously updated knowledge near individual remote IP network segments. Only the router that acts as the default gateway needs to maintain this level of routing knowledge to accomplish other remote network segments in the larger internetwork. If the default gateway fails, communication across the local network segment may be impaired. To prevent this, you can utilize the Advanced TCP/IP Settings dialog box (in Network Connections) for each connection to specify multiple default gateways. Y'all can likewise use the route command to manually add routes to the routing table for heavily used hosts or networks. If you accept multiple interfaces and you configure a default gateway for each interface, TCP/IP by default automatically calculates an interface metric that is based on the speed of the interface. The interface metric becomes the metric of the default route in the routing tabular array for the configured default gateway. The interface with the highest speed has the everyman metric for its default route. The result is that whenever multiple default gateways are configured on multiple interfaces, the fastest interface volition exist used to forrard traffic to its default gateway. If multiple interfaces of the same speed have the aforementioned everyman interface metric, then, based upon the binding lodge, the default gateway of the kickoff network adapter is used. The default gateway for the second network adapter is used when the showtime is unavailable. In social club for Host A on Network i to communicate with Host B on Network 2, Host A kickoff checks its routing table to see if a specific road to Host B exists. If there is no specific route to Host B, Host A frontwards its TCP/IP traffic for Host B to its own default gateway, IP Router i.

http://technet.microsoft.com/en-united states/library/cc779696%28v=ws.10%29.aspx
http://technet.microsoft.com/en-us/library/cc958877.aspx
http://back up.microsoft.com/kb/299540/en-united states
QUESTION 163
Your network contains an Active Directory domain named contoso.com. The domain contains a server named Server1. Server1 runs Windows Server 2012 R2 and has the Hyper-V server office installed. You need to log the amount of organisation resources used by each virtual machine. What should you lot practise?
A. From Windows PowerShell, run the Enable-VMRe5ourceMetering cmdlet.
B. From Windows System Resource Manager, enable Bookkeeping.
C. From Windows Arrangement Resource Managing director, add together a resource allocation policy.
D. From Windows PowerShell, run the Measure-VM cmdlet.
Reply: A
Explanation:
http://technet.microsoft.com/en-united states of america/library/cc779696%28v=ws.x%29.aspx
http://technet.microsoft.com/en-us/library/cc958877.aspx
http://support.microsoft.com/kb/299540/en-us
QUESTION 164
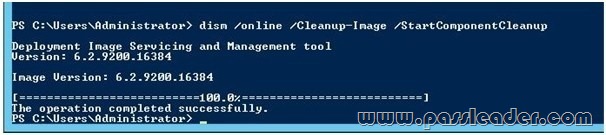
You take a server named Server1 that runs Windows Server 2012 R2. You programme to create an image of Server1. You demand to remove the source files for all server roles that are not installed on Server1. Which tool should you use?
A. servermanagercmd.exe
B. imagex.exe
C. dism.exe
D. ocsetup.exe
Answer: C
Explanation:
servermanagercmd.exe – The servermanagercmd.exe command-line tool has been deprecated in Windows Server 2008 R2.
imagex.exe – ImageX is a command-line tool in Windows Vista that you can apply to create and manage Windows image (.wim) files. A .wim file contains one or more volume images, disk volumes that incorporate images of an installed Windows operating system.
dism.exe – Deployment Image Servicing and Direction (DISM.exe) is a control-line tool that can be used to service a Windows image or to prepare a Windows Preinstallation Environment (WindowsPE) image. Information technology replaces Package Managing director (pkgmgr.exe), PEimg, and Intlcfg that were included in Windows Vista. The functionality that was included in these tools is now consolidated in 1 tool (DISM.exe), and new functionality has been added to improve the experience for offline servicing. DISM can Add, remove, and enumerate packages.
ocsetup.exe – The ocsetup.exe tool is used as a wrapper for Package Managing director (pkgmgr.exe) and for WindowsInstaller (Msiexec.exe). ocsetup.exe is a command-line utility that tin be used to perform scripted installs and scripted uninstalls of Windows optional components. The ocsetup.exe tool replaces the sysocmgr.exe tool that Windows XP and Windows Server 2003 use.
http://technet.microsoft.com/en-united states/library/hh824822.aspx
http://blogs.technet.com/b/joscon/archive/2010/08/26/adding-features-with-dism.aspx
http://technet.microsoft.com/en-u.s./library/hh831809.aspx
http://technet.microsoft.com/en-usa/library/hh825265.aspx
QUESTION 165
Your network contains an Active Directory domain named contoso.com. An administrator provides you with a file that contains the information to create user accounts for 200 temporary employees. The file is shown in the showroom. (Click the Exhibit button.)

Yous demand to automate the creation of the user accounts. You must achieve this goal by using the minimum corporeality of administrative effort. Which tool should yous use?
A. csvde
B. Internet user
C. Ldifde
D. Dsadd
Respond: A
Explanation:
csvde – Imports and exports data from Active Directory Domain Services (Advertizing DS) using files that store data in the comma-separated value (CSV) format. Yous can also back up batch operations based on the CSV file format standard.
http://technet.microsoft.com/en-us/library/cc732101(v=ws.10).aspx
Internet user – Adds or modifies user accounts, or displays user account information.
http://technet.microsoft.com/en-us/library/cc771865(5=ws.10).aspx
Ldifde – Creates, modifies, and deletes directory objects. You tin too utilize ldifde to extend the schema, export Agile Directory user and group data to other applications or services, and populate Active Directory Domain Services (AD DS) with data from other directory services.
http://technet.microsoft.com/en-us/library/cc731033(v=ws.10).aspx
Dsadd – Adds specific types of objects to the directory.
http://technet.microsoft.com/en-united states of america/library/cc753708(v=ws.10).aspx
csvde.exe is the best selection to add multiple users. as y'all just need to consign the excel spreadsheet as a csv file and make certain the parameters are correct. You can use Csvde to import and export Active Directory information that uses the comma-separated value format. Utilize a spreadsheet programme such equally Microsoft Excel to open this .csv file and view the header and value information

http://support.microsoft.com/kb/327620/en-united states
QUESTION 166
Hotspot Question
Your network contains an Active Directory domain named contoso.com. All client computers run Windows eight. An administrator creates an awarding control policy and links the policy to an organizational unit (OU) named OU1. The application control policy contains several deny rules. The deny rules use to the Anybody group. You lot need to prevent users from running the denied application. What should you configure? To answer, select the appropriate object in the answer expanse.
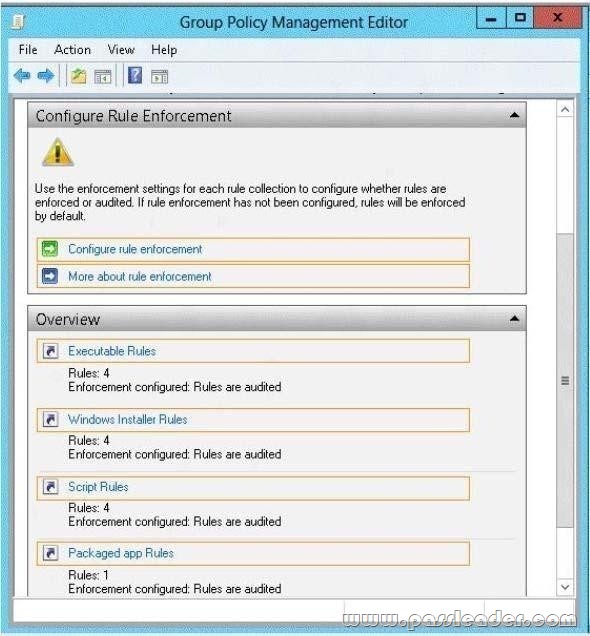
Answer:

Caption:
To enable the enforce rules enforcement setting by using the Local Security Policy snap-in:
1. Click Start, type secpol.msc in the search programs and files box, so press ENTER.
2. If the User Account Command dialog box appears, confirm that the activity it displays is what you desire, and so click Yep.
iii. In the console tree, double-click Application Control Policies, right-click AppLocker, and then click Properties.
four. On the Enforcement tab, select the Configured cheque box for the rule collection that y'all want to enforce, and then verify that Enforce rules is selected in the listing for that rule collection.
5. Repeat step 4 to configure the enforcement setting to Enforce rules for additional rule collections.
6. Click OK.
http://technet.microsoft.com/en-united states of america/library/ee791885(v=ws.10).aspx
QUESTION 167
You accept a impress server named Server1 that runs Windows Server 2012 R2. You observe that when there are many pending print jobs, the arrangement drive occasionally runs out of free space. You add a new hard disk to Server1. You create a new NTFS volume. You demand to prevent the impress jobs from consuming disk infinite on the system volume. What should you alter?
A. the properties of the Print Spooler service
B. the Print Server Properties
C. the properties of each shared printer
D. the properties on the new volume
Answer: B
Caption:
Windows spools print jobs by default to the following directory equally the they are processed:
%SystemRoot%\SYSTEM32\SPOOL\PRINTERS.
It is possible for the ambassador of a Windows print server to manually instruct Windows the location forplacing the spool files, if for example there is a business organization for disk space.

http://back up.microsoft.com/kb/137503/en-u.s.a.
http://technet.microsoft.com/en-us/library/cc757764%28v=ws.10%29.aspx
http://technet.microsoft.com/en-usa/library/cc736979%28v=ws.10%29.aspx
QUESTION 168
Your network contains an Active Directory domain named contoso.com. The domain contains an application server named Server1. Server1 runs Windows Server 2012 R2. You have a client awarding named App1 that communicates to Server1 past using dynamic TCP ports. On Server1, a technician runs the post-obit command:
New-NetFirewallRule -DisplayName AllowDynamic -Management Outbound -LocalPort 1024- 65535 -Protocol TCP
Users study that they tin can no longer connect to Server1 by using App1.You need to ensure that App1 can connect to Server1. What should you run on Server1?
A. Set-NetFirewallRule -DisplayName AllowDynamic -Action Allow
B. netsh advfirewall firewall set up rule name=allowdynamic new action=allow
C. Set-NetFirewallRule -DisplayName AllowDynamic -Management Inbound
D. netsh advfirewall firewall add together rule name=allowdynamic activity=allow
Answer: C
Explanation:
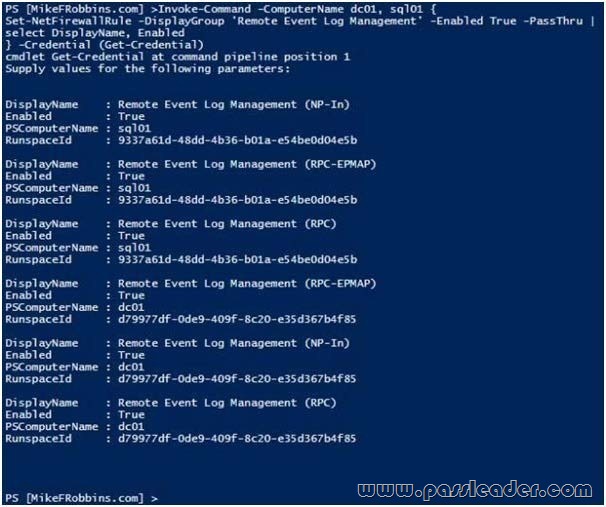
Set-NetFirewallRule – Modifies existing firewall rules. Y'all accept to allow the connexion INTO the server – inbound rules.
http://technet.microsoft.com/en-us/library/jj573828%28v=wps.620%29.aspx
http://mikefrobbins.com/2013/02/28/apply-powershell-to-remotely-enable-firewall-exceptionson-windows-server-2012/
QUESTION 169
You accept a server named dc2.contoso.com that runs Windows Server 2012 R2 and has the DNS Server server role installed. You open DNS Manager as shown in the exhibit. (Click the Exhibit button.)
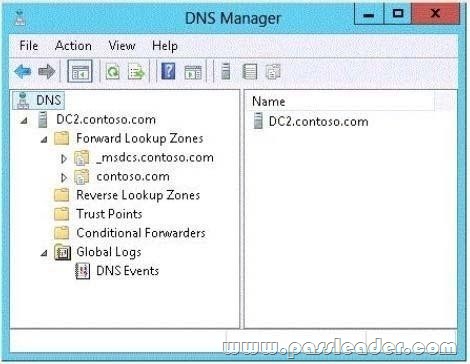
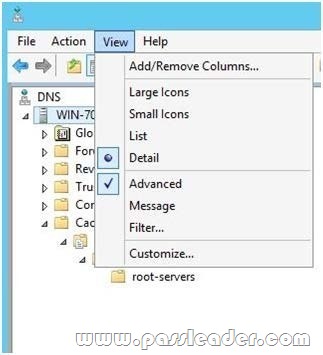
You need to view the DNS server enshroud from DNS Manager. What should you do first?
A. From the View carte, click Advanced.
B. From the Action menu, click Configure a DNS Server.
C. From the View carte, click Filter.
D. From the Action menu, click Properties.
Answer: A
Explanation:
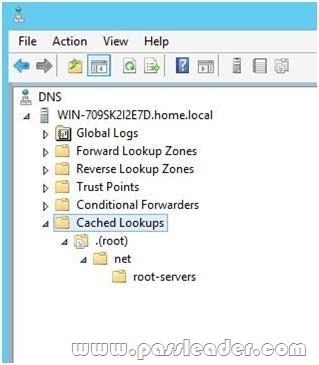
To view the contents of the DNS enshroud, perform the post-obit steps:
ane. Showtime the Microsoft Management Console (MMC) DNS snap-in (Go to Start, Programs, Authoritative Tools, and click DNS).
two. From the View menu, select Advanced.
three. Select the Cached Lookups tree node from the left-hand pane to brandish the top-level domains (e.g., com, cyberspace) nether .(root). Aggrandize any of these domains to view the buried DNS information (the actual records volition appear in the right-manus pane).
QUESTION 170
You lot work equally an administrator at contoso.com. The contoso.com network consists of a single domain named contoso.com. All servers on the contoso.com network have Windows Server 2012 R2 installed. contoso.com has a server, named PL-SR07, which has two physical disks installed. The C: drive hosts the boot division, while the D: bulldoze is not being used. Both disks are online. You have received instructions to create a virtual automobile on PL-SR07. Subsequent to creating the virtual machine, yous accept to connect the D: drive to the virtual automobile. Which of the following is TRUE with regards to connecting a physical disk to a virtual machine?
A. The physical disk should not be online.
B. The physical deejay should exist uninstalled and re-installed.
C. The physical disk should exist configured as a striped disk.
D. The physical disk should exist configured as a mirrored disk.
Reply: A
Explanation:
Your virtual machines can besides be connected to physical hard disks on the virtualization server virtual hard disks. (This is sometimes referred to as having a "pass-through" deejay connected to a virtual motorcar.) The physical hard deejay that y'all connect to a virtual machine tin can also exist a network-attached disk, similar a logical unit of measurement number (LUN) in a storage area network (SAN). A common example is an iSCSI LUN that has been mapped to the virtualization server by using Microsoft iSCSI Initiator. Because the virtualization server sees network-attached storage as local disks, the iSCSI LUN can be continued to a virtual machine. The most important limitation about having a physical difficult disk continued to a virtual automobile is that it cannot be connected to the virtualization server or to other virtual machines at the aforementioned time. The virtual car must have exclusive access to the physical hard disk.
Pass-through Disk Configuration
Hyper-Five allows virtual machines to access storage mapped directly to the Hyper-V server without requiring the volume be configured. The storage can either be a concrete disk internal to the Hyper-5 server or it tin be a Storage Area Network (SAN) Logical Unit of measurement (LUN) mapped to the Hyper-V server. To ensure the Guest has sectional access to the storage, information technology must exist placed in an Offline state from the Hyper-Vserver perspective.
http://blogs.technet.com/b/askcore/archive/2008/ten/24/configuring-laissez passer-through-disks-in-hyper-v.aspx
http://technet.microsoft.com/pt-pt/library/ff404147%28v=ws.10%29.aspx
QUESTION 171
Your network contains an Active Directory domain named contoso.com. The domain contains a server named Server1 that runs Windows Server 2012 R2. Y'all create a new inbound dominion by using Windows Firewall with Advanced Security. You need to configure the dominion to permit Server1 to accept unsolicited inbound packets that are received through a network accost translation (NAT) device on the network. Which setting in the rule should you configure?
A. Edge traversal
B. Authorized computers
C. Interface types
D. Remote IP address
Answer: A
Explanation:
Border traversal – This indicates whether border traversal is enabled (Yes) or disabled (No). When edge traversal is enabled, the application, service, or port to which the rule applies is globally addressable and accessible from outside a network address translation (NAT) or edge device.

Select one of the following options from the list:
Cake border traversal (default) – Foreclose applications from receiving unsolicited traffic from the Internet through a NAT edge device.
Allow edge traversal – Allow applications to receive unsolicited traffic direct from the Internet through a NAT border device.
Defer to user – Permit the user decide whether to allow unsolicited traffic from the Internet through a NAT border device when an awarding requests it.
Defer to application – Let each application determine whether to let unsolicited traffic from the Internet through a NAT edge device.
http://technet.microsoft.com/en-us/library/cc731927.aspx
http://technet.microsoft.com/en-us/library/dd421713%28v=ws.ten%29.aspx
QUESTION 172
Your network contains an Active Directory domain named contoso.com. The domain contains a member server named Server1. Server1 runs Windows Server 2012 R2 and has the File Server server role installed. On Server1, you create a share named Documents. You need to ensure that users can recover files that they accidently delete from Documents. What should you lot do?
A. Enable shadow copies by using Computer Direction.
B. Modify the Startup blazon of the Volume Shadow Copy Service (VSS) by using the Services panel.
C. Create a recovery partition by using Windows Cess and Deployment Kit (Windows ADK).
D. Create a storage puddle that contains a two-manner mirrored volume past using Server Manager.
Respond: A
Explanation:
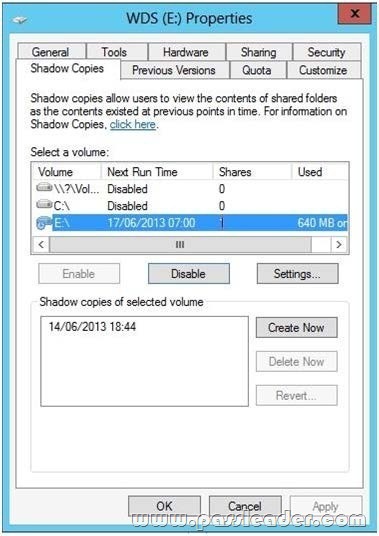
If you enable Shadow Copies of Shared Folders on a book using the default values, a chore volition exist scheduled to create shadow copies at 7:00 A.M of side by side business day. The default storage surface area will be on the same volume, and its size will be ten percent of the available infinite. You can but enable Shadow Copies of Shared Folders on a per-volume basis — that is, you cannot select specific shared folders and files on a volume to be copied or not copied. To enable and configure Shadow Copies of Shared Folders:
ane. Click Outset, betoken to Authoritative Tools, and then click Computer Management.
ii. In the console tree, right-click Shared Folders, click All Tasks, and then click Configure Shadow Copies.
3. In Select a volume, click the volume that you desire to enable Shadow Copies of Shared Folders for, and so click Enable.
4. Yous will see an alert that Windows will create a shadow copy now with the current settings and that the settings might not exist advisable for servers with high I/O loads. Click Yes if you desire to go on or No if youwant to select a different book or settings.
5. To make changes to the default schedule and storage area, click Settings.
http://technet.microsoft.com/en-us/library/cc771893.aspx
QUESTION 173
You have a server named Server1 that runs a Server Cadre installation of Windows Server 2012 R2. Server1 is configured to obtain an IPv4 address by using DHCP. You need to configure the IPv4 settings of the network connexion on Server1 as follows:
– IP accost: 10.1.1.i
– Subnet mask: 255.255.240.0
– Default gateway: ten.ane.ane.254
What should you lot run?
A. netsh.exe
B. netcfg.exe
C. msconfig.exe
D. ipconfig.exe
Answer: A
Explanation:
In gild to configure TCP/IP settings such as the IP address, Subnet Mask, Default Gateway, DNS and WINS addresses and many other options you tin can use netsh.exe.
Incorrect:
Non D: Windows Server 2012 Core still has IPCONFIG.EXE that tin be used to view the IP configuration. Modern servers typically come with several network interface ports. This causes IPCONFIG.EXE to scroll off the screen when viewing its output. Consider piping the output if IPCONFIG.EXE to a file and view it with notepad.exe.
QUESTION 174
Your network contains an Active Directory domain named contoso.com. The domain contains three member servers. The servers are configured as shown in the following table.
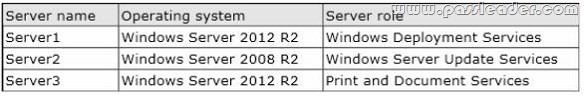
All client computers run Windows 8. All customer computers receive updates from Server2. On Servers, you add a shared printer named Printer1. Printer1 uses a Type four commuter that is not included in the Windows eight installation media. You need to ensure that when users connect to the printer for the first fourth dimension, the printer commuter is installed automatically on their customer computer. What should you practise?
A. From the Windows Deployment Services console on Server1, add the commuter packet for Printer1.
B. From the Update Services console on Server2, import and approve updates.
C. From Windows PowerShell on Server3, run the Add-PrinterDriver cmdlet.
D. From the Impress Direction panel on Server3, add together boosted drivers for Printer1.
Answer: D
Explanation:
Print and Certificate Services enables you lot to centralize impress server and network printer tasks. With this role, you lot can likewise receive scanned documents from network scanners and road the documents to a shared network resource, Windows SharePoint Services site, or electronic mail addresses. Starting with Windows eight and Server 2012 R2 – here comes the Version 4 drivers (form commuter or model specific commuter) which changes a couple of things, a system that allows people to install their printers without having to locate a commuter for that device in many cases.
1. In that location is no v3 driver support for Windows on ARM
two. The print server is no longer a software distribution mechanism
three. Grouping Policy Preference TCP/IP printers do non support Type 4 print drivers
iv. The LPR/LPD protocol is deprecated and will eventually be removed
To install v4 drivers using the Impress Management Console:
ane. Open the Print Management Console past opening Server Manager, click Tools, and then click Print Management.
2. Expand Print Servers, so aggrandize the Print Server proper name. Right click Drivers and select Add Drivers.
3. To add a v4 commuter for a device, select the driver that has v4 or Course Driver in the name.
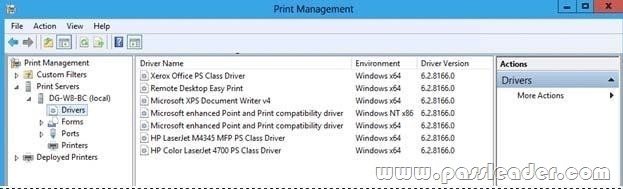
Once installed, v4 drivers are identified past the Version field displayed in the Commuter Backdrop:

The driver proper name will state Grade Driver, the Config File should show PrintConfig.dll, and the commuter path should be %systemroot%\system32\DriverStore.
Class Drivers – V4 drivers that ship with Windows Server 2012 R2 are known as Class Drivers. Drivers of this type should e'er display Form Driver in the name.
Model Specific Drivers – V4 drivers that are downloaded directly from a printer manufacturer website or downloaded from Windows Update are known as model specific drivers.
http://technet.microsoft.com/en-us/library/hh831468.aspx
http://technet.microsoft.com/en-us/library/jj134163.aspx
http://technet.microsoft.com/en-united states of america/library/hh831769.aspx
http://blogs.technet.com/b/askperf/annal/2012/11/03/windows-8-windows-server-2012-what-south-new-with-press-in-windows-viii.aspx
QUESTION 175
Your network contains an Active Directory domain named contoso.com. The domain contains twenty calculator accounts in an organizational unit (OU) named OU1. A user business relationship named User1 is in an OU named OU2. Y'all are configuring a Group Policy Object (GPO) named GPO1. You need to assign User1 the Support files and directories user right to all of the reckoner accounts in OU1. Which two actions should you perform? (Each correct answer presents function of the solution. Choose two.)
A. Link GPO1 to OU1.
B. Link GPO1 to OU2.
C. Modify the Delegation settings of GPO1.
D. From User Configuration in GPO1, modify the security settings.
Eastward. From Estimator Configuration in GPO1, alter the security settings.
Answer: AE
Explanation:
A. You lot have to Link a GPO to an object in social club for information technology to be Applied to that object.
B. Incorrect object to link the GPO.
C. Delegation settings refer to delegating control over the properties of the GPO.
D. User Configuration typically contains subitems for Software Settings, Windows Settings, and AdministrativeTemplates.
Eastward. Backup Files and Directories are constitute in Computer Configuration\Windows Settings\Local Policies\User Rights Assignment Dorsum up files and directories – this user right determines which users can bypass file and directory, registry,and other persistent object permissions for the purposes of backing upward the system.

Specifically, this user right is similar to granting the post-obit permissions to the user or group in question on all files and folders on the system:
– Traverse Folder/Execute File
– List Folder/Read Information
– Read Attributes
– Read Extended Attributes
– Read Permissions
Caution: Assigning this user correct can be a security risk. Since in that location is no style to exist sure that a user is backing up information, stealing data, or copying information to be distributed, just assign this user right to trusted users.
Default on workstations and servers: Administrators, Backup Operators.
Default on domain controllers: Administrators, Backup Operators, Server Operators.
http://www.microsoft.com/en-us/download/details.aspx?id=25250
QUESTION 176
You have an existing Active Directory site named Site1. You create a new Active Directory site and name information technology Site2. Yous need to configure Agile Directory replication between Site1 and Site2. Y'all install a new domain controller. You create the site link between Site1 and Site2. What should you do next?
A. Use the Active Directory Sites and Services console to configure a new site link span object.
B. Use the Agile Directory Sites and Services console to decrease the site link cost between Site1 and Site2.
C. Use the Active Directory Sites and Services console to assign a new IP subnet to Site2. Motion the new domain controller object to Site2.
D. Employ the Active Directory Sites and Services console to configure the new domain controller as a preferred bridgehead server for Site1.
Reply: C
Caption:
http://www.enterprisenetworkingplanet.com/netsysm/article.php/624411/Intersite-Replication.htm
Inter-site Replication
The procedure of creating a custom site link has fivebasic steps:
one. Create the site link.
2. Configure the site link'south associated attributes.
iii. Create site link bridges.
4. Configure connection objects. (This step is optional.)
v. Designate a preferred bridgehead server. (This step is optional.)
http://technet.microsoft.com/en-us/library/cc759160%28v=ws.x%29.aspx
QUESTION 177
Your company has an Active Directory wood. Not all domain controllers in the woods are configured every bit Global Itemize Servers. Your domain structure contains one root domain and one child domain. You lot modify the folder permissions on a file server that is in the kid domain. You discover that some Access Control entries kickoff with S-one-5-21 and that no business relationship proper noun is listed. You demand to listing the account names. What should yous do?
A. Movement the RID master role in the child domain to a domain controller that holds the Global Catalog.
B. Modify the schema to enable replication of the friendlynames attribute to the Global Catalog.
C. Motility the RID master role in the kid domain to a domain controller that does not hold the Global Catalog.
D. Move the infrastructure master office in the child domain to a domain controller that does not hold the Global Catalog.
Answer: D
Explanation:
If the IM Flexible Single Master Functioning (FSMO) role holder is too a global catalog server, the phantom indexes are never created or updated on that domain controller. (The FSMO is as well known as the operations master.) This behavior occurs because a global itemize server contains a partial replica of every object in Active Directory. The IM does non shop phantom versions of the foreign objects because it already has a partial replica of the object in the local global catalog. For this process to work correctly in a multidomain surroundings, the infrastructure FSMO function holder cannot be a global itemize server. Be enlightened that the first domain in the forest holds all five FSMO roles and is also a global itemize. Therefore, you must transfer either role to some other computer as soon as another domain controller is installed in the domain if you plan to have multiple domains.
QUESTION 178
Your company has an Active Directory domain. You lot log on to the domain controller. The Active Directory Schema snap-in is non available in the Microsoft Management Console (MMC). Y'all need to access the Active Directory Schema snap-in. What should you do?
A. Annals Schmmgmt.dll.
B. Log off and log on again past using an account that is a fellow member of the Schema Admins grouping.
C. Use the Ntdsutil.exe command to connect to the schema chief operations master and open up the schema for writing.
D. Add the Active Directory Lightweight Directory Services (Advertizing/LDS) role to the domain controller by using Server Managing director.
Answer: A
Caption:
Install the Active Directory Schema Snap-In
You lot tin use this process to first register the dynamic-link library (DLL) that is required for the Active Directory Schema snap-in. You can and so add the snap-in to Microsoft Management Console (MMC). To install the Active Directory Schema snap-in:
one. To open an elevated command prompt, click Starting time, type command prompt and then correct-click Command Prompt when information technology appears in the Showtime menu. Next, click Run every bit ambassador and and then click OK. To open an elevated command prompt in Windows Server 2012 R2, click Kickoff, type cmd, right click cmd then click Run every bit ambassador
two. Blazon the post-obit command, and and so press ENTER: regsvr32 schmmgmt.dll
3. Click Offset, click Run, blazon mmc and then click OK
iv. On the File menu, click Add/Remove Snap-in
5. Under Available snap-ins, click Active Directory Schema, click Add and so click OK
6. To salvage this panel, on the File menu, click Save
seven. In the Save Every bit dialog box, practise i of the post-obit:
* To identify the snap-in in the Administrative Tools folder, in File proper name, type a name for the snap-in, and then click Salvage.
* To salve the snap-in to a location other than the Authoritative Tools folder, in Save in, navigate to a location for the snap-in. In File name, type a name for the snap-in, and and so click Save.
QUESTION 179
Your network contains a domain controller that is configured as a DNS server. The server hosts an Active Directory-integrated zone for the domain. You need to reduce how long it takes until dried records are deleted from the zone. What should you practise?
A. From the configuration directory partition of the wood, modify the tombstone lifetime.
B. From the configuration directory division of the wood, modify the garbage collection interval.
C. From the aging properties of the zone, modify the no-refresh interval and the refresh interval.
D. From the start of potency (SOA) record of the zone, change the refresh interval and the expire interval.
Answer: C
Explanation:
Scavenging automates the deletion of old records. When scavenging is enabled, then you should also change the no-refresh and refresh intervals of the aging properties of the zone else information technology may take as well long for stale records to be deleted and the size of the DNS database tin can become big and accept an adverse effect on operation.
QUESTION 180
Yous have an Agile Directory domain named contoso.com. You take a domain controller named Server1 that is configured as a DNS server. Server1 hosts a standard main zone for contoso.com. The DNS configuration of Server1 is shown in the exhibit. You lot discover that stale resource records are not automatically removed from the contoso.com zone. You need to ensure that the stale resource records are automatically removed from the contoso.com zone. What should y'all practice?

A. Prepare the scavenging menstruation of Server1 to 0 days.
B. Modify the Server Aging/Scavenging backdrop.
C. Configure the aging properties for the contoso.com zone.
D. Convert the contoso.com zone to an Agile Directory-integrated zone.
Answer: C
Explanation:
Scavenging or aging equally information technology is also known as automates the deletion of former records. When scavenging is disabled, these records must be deleted manually or the size of the DNS database tin become large and have an adverse effect on functioning. In the showroom it shows that scavenging is enabled on Server1, thus you should configure the aging properties for the zone.
QUESTION 181
Hotspot Question
Your network contains 2 servers named Server1 and Server2 that run Windows Server 2012 R2. Server1 has the Hyper-Five server function installed. Server2 has the Windows Deployment Services server role installed. On Server1, yous accept a virtual machine named VM1. You plan to deploy an epitome to VM1 by using Windows Deployment Services (WDS). You need to ensure that VM1 can connect to Server1 by using PXE. Which settings should you lot configure on VM1? To answer, select the appropriate settings in the answer area.

Respond:
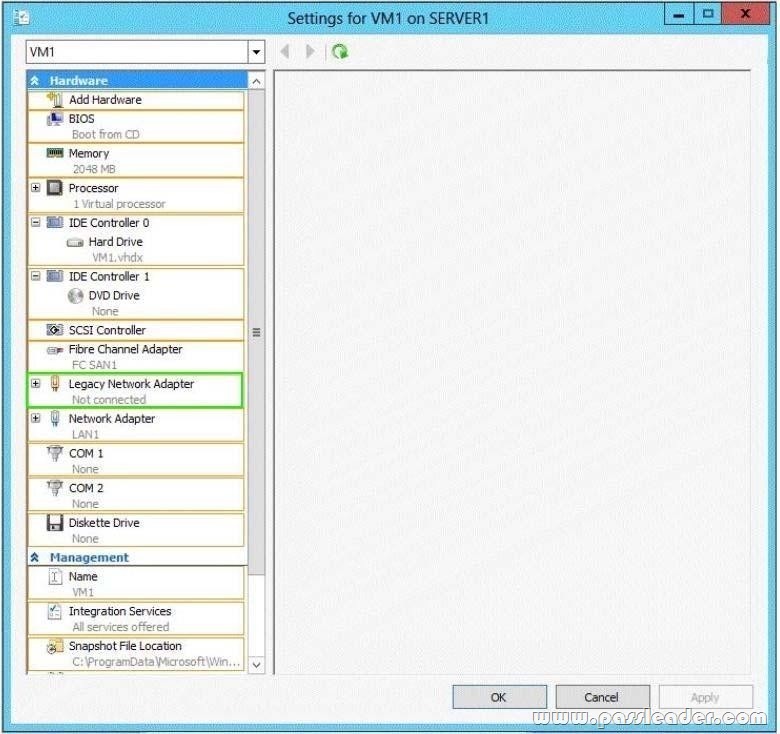
Explanation:
Virtual machines can be deployed to Hyper-V using Windows Deployment Services (WDS). To accomplish this requires the proper WDS infrastructure be in place and that the VM PXE boot using a Legacy Network Adapter. By default, there is only a "Standard Network Adapter" installed on the Virtual Machine, but for PXE functionality you lot volition demand to add together a "Legacy Network Adapter". Become to the "Legacy Network Adapter" that you merely added and specify that it should use the Virtual Switch that you lot but created. Last but not least, you should alter the BIOS boot priority to brand sure that the Virtual Auto always tries to boot first using the "Legacy Network Adapter". Only select the "Legacy Network Adapter" and move it to the tiptop using the buttons.
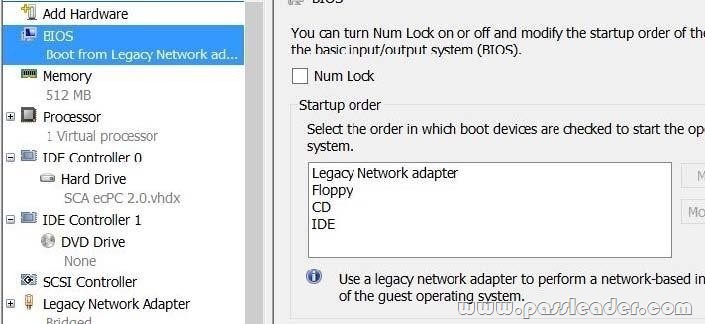
Start your Virtual Machine and now PXE boot should work.
http://world wide web.danielclasson.com/guide-how-to-get-pxe-boot-to-work-in-hyper-v/
http://blogs.technet.com/b/askcore/archive/2008/eleven/25/installing-a-vm-operating-arrangement-using-a-legacy-network-adapter-and-pxe-boot.aspx
QUESTION 182
Hotspot Question
Your network contains an Active Directory domain named contoso.com. You need to identify whether the Company attribute replicates to the global catalog. Which part of the Active Directory partition should you lot view? To respond, select the appropriate Agile Directory object in the respond surface area.
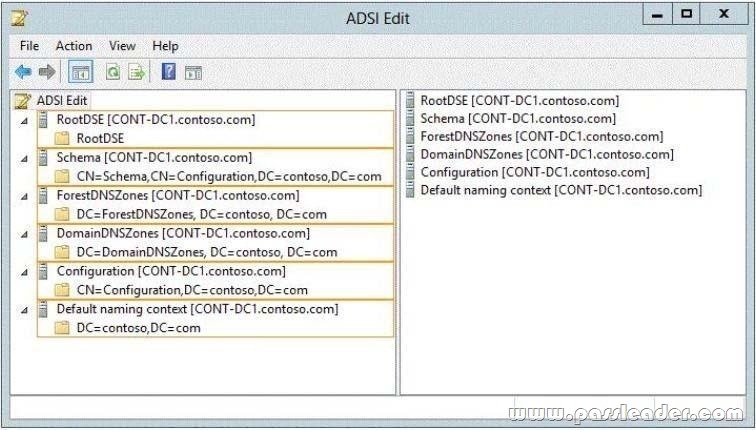
Answer:
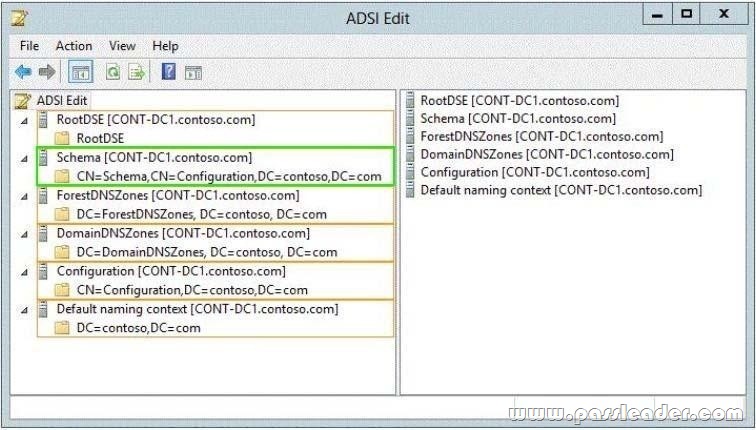
Explanation:
Schema – Contains the Schema container, which stores class and attribute definitions for all existing and possible Agile Directory objects in cn=schema,cn=configuration,dc=forestRootDomain. Updates to this container are replicated to all domain controllers in the forest. You can view the contents of the Schema container in the Active Directory Schema console.
http://technet.microsoft.com/en-us/library/cc961591.aspx
QUESTION 183
Hotspot Question
Y'all accept a server named Server1. Server1 runs Windows Server 2012 R2 and has the Windows Deployment Services (WDS) server role installed. You lot install the DHCP Server server role on Server1. You need to ensure that Server1 can answer to DHCP clients and WDS clients. What should you lot configure for the DHCP service and the WDS service? To answer, configure the appropriate options in the answer area.

Answer:
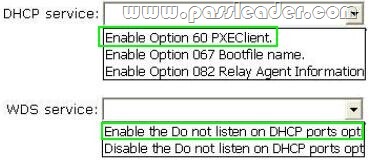
Explanation:
Traditionally, simply DHCP listened on port UDP 67, but now WDS also listens on port UDP 67 WDS and DHCP are installed on the same server: You must tell WDS not to heed on port UDP 67, leaving information technology available for DHCP traffic only. Simply so how does the client discover the WDS server? You prepare option 60 in DHCP. The DHCP option 60, when prepare to "PXEClient" is used only to instruct the PXE clients to try to use a PXE Service bound on UDP port 4011. Actually, if in that location is a bootp or dhcp service bound on UDP port 67 of an host (usually called a server), a PXE service cannot bind on that port on that host. Since the PXE Service uses BOOTP/DHCP packets to send the options 66 and 67 to the clients, it needs to be able to bind to the associated port (bootps) or to an alternated port (4011) that the clients know they must use as the alternating port. And to instruct the clients to use this alternating port, you have to prepare dhcp selection 60 to "PXEClient". If Windows Deployment Services and DHCP are running on the same computer, configuring Windows Deployment Services to not reply to whatsoever client computers will not work. This is because although Windows Deployment Services will not answer, DHCP volition. You should disable WDS if you take both installed and using DHCP.
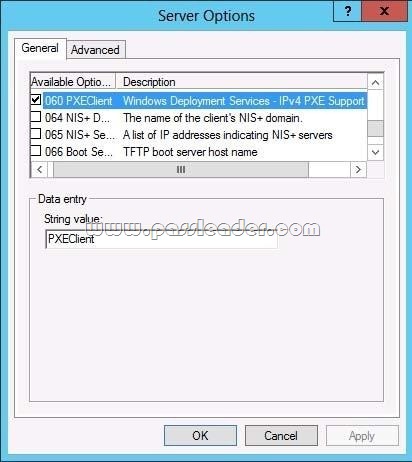
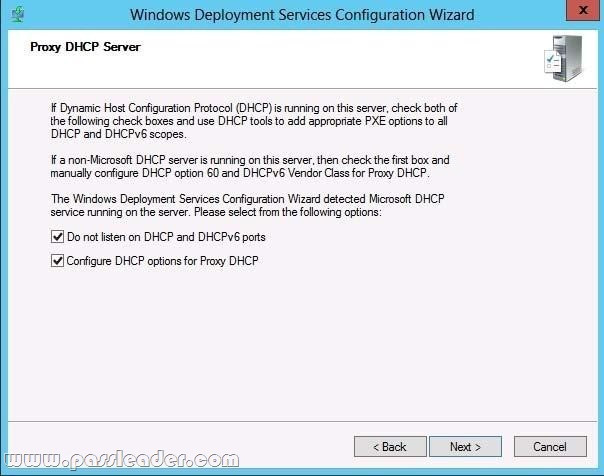
To configure Windows Deployment Services to run on the same computer every bit Microsoft DHCP: Correct-click the server and click Properties. On the DHCP tab, select Practise not listen on port 67 and Configure DHCP Option #60 Tag to PXEClient. This procedure does the following: HKEY_LOCAL_MACHINE\Organisation\CurrentControlSet\Services\WDSServer\Parameters\UseDhcpPorts to 0. Adds the option 60 PXEClient tag to all of your DHCP scopes.
http://gallery.technet.microsoft.com/DHCP-Option-60-Configuratio-2cad825d
QUESTION 184
Hotspot Question
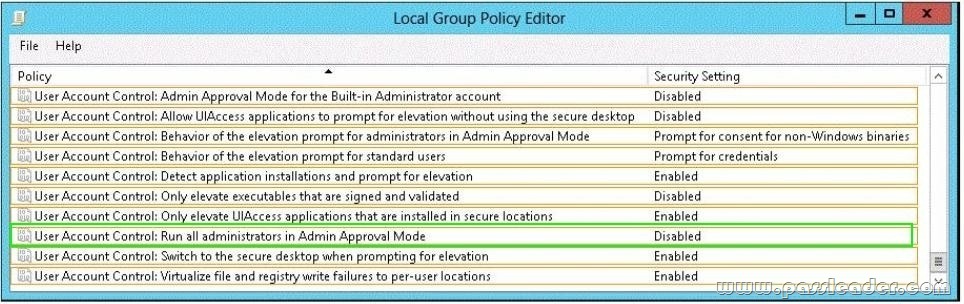
You accept a server named Server1. Server1 runs Windows Server 2012 R2. A user named Admin1 is a member of the local Administrators group. You need to ensure that Admin1 receives a User Account Control (UAC) prompt when attempting to open Windows PowerShell as an administrator. Which setting should you modify from the Local Group Policy Editor? To answer, select the appropriate setting in the reply surface area.

Respond:
QUESTION 185
You have a server that runs Windows Server 2012 R2. The server contains the disks configured as shown in the post-obit table.

You need to create a volume that tin store upwardly to 3 TB of user files. The solution must ensure that the user files are available if one of the disks in the volume fails. What should you create?
A. a storage puddle on Disk 2 and Disk three
B. a spanned book on Disk ii and Disk 3
C. a mirrored volume on Disk ane and Deejay iii
D. a mirrored volume on Disk two and Disk 3
E. a RAID-five book on Disk 1, Disk 2, and Disk three
F. a storage pool on Deejay i and Disk 3
G. a spanned volume on Disk 0 and Disk 4
H. a mirrored volume on Disk i and Disk 4
Answer: D
QUESTION 186
You have a server that runs Windows Server 2012 R2. The server contains the disks configured as shown in the post-obit tabular array.

You demand to create a volume that can store up to 3 TB of user files. The solution must ensure that the user files are available if one of the disks in the volume fails. What should you create?
A. A mirrored volume on Disk ane and Deejay 4
B. A storage puddle on Deejay two and Deejay three
C. A storage pool on Disk 1 and Disk iii
D. A mirrored volume on Deejay 2 and Disk three
Answer: D
Explanation:
A mirrored volume provides an identical twin of the selected book. All data written to the mirrored volume is written to both volumes, which results in disk capacity of only 50 percentage. Whatsoever book can be mirrored, including the organization and kicking volumes. The disk that you select for the shadow volume does non demand to be identical to the original deejay in size, or in its number of tracks and cylinders. This means that you do non have to supercede a failed disk with an identical model. The unused surface area that y'all select for the shadow volume cannot exist smaller than the original volume. If the area that you select for the shadow volume is larger than the original, the extra space on the shadow disk can exist configured equally some other volume. Dynamic disks provide features that basic disks exercise non, such as the power to create volumes that span multiple disks (spanned and striped volumes) and the ability to create fault-tolerant volumes (mirrored and RAID-5 volumes). The post-obit operations can be performed only on dynamic disks:
– Create and delete simple, spanned, striped, mirrored, and RAID-5 volumes.
– Extend a simple or spanned book.
– Remove a mirror from a mirrored volume or interruption the mirrored volume into two volumes.
– Repair mirrored or RAID-v volumes.
– Reactivate a missing or offline deejay.
You demand at to the lowest degree two dynamic disks to create a mirrored volume. Mirrored volumes are fault tolerant and utilise RAID-1, which provides back-up past creating two identical copies of a volume. Mirrored volumes cannot be extended. Both copies (mirrors) of the mirrored volume share the same bulldoze letter.

http://technet.microsoft.com/en-u.s.a./library/cc779765%28v=ws.10%29.aspx
http://msdn.microsoft.com/en-u.s.a./library/windows/desktop/aa363785%28v=vs.85%29.aspx
http://technet.microsoft.com/en-us/library/cc938487.aspx
QUESTION 187
Hotspot Question
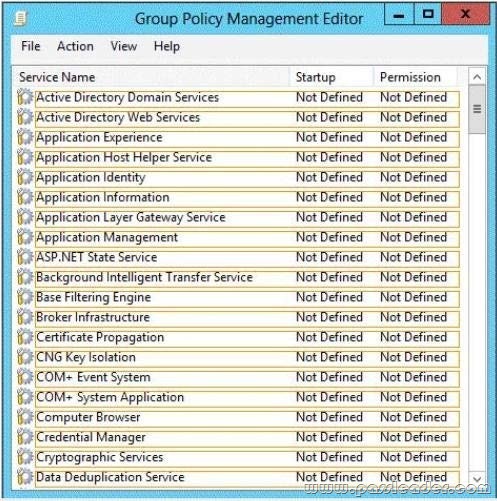
Your network contains an Agile Directory domain named adatum.com. All domain controllers run Windows Server 2012 R2. All client computers run Windows 7. The calculator accounts for all of the customer computers are located in an organizational unit of measurement (OU) named OU1. An administrator links a Group Policy Object (GPO) to OU1. The GPO contains several application control policies. You discover that the awarding control policies are not enforced on the client computers. You need to modify the GPO to ensure that the application control policies are enforced on the client computers. What should you lot configure in the GPO? To respond, select the appropriate service in the answer surface area.
Reply:

Explanation:
Does AppLocker use any services for its rule enforcement? Yeah, AppLocker uses the Application Identity service (AppIDSvc) for rule enforcement. For AppLocker rules to be enforced, this service must be set to beginning automatically in the GPO.
http://technet.microsoft.com/en-united states/library/ee619725%28v=ws.10%29.aspx
QUESTION 188
Your network contains an Active Directory domain named contoso.com. The domain contains iii servers named Server1, Served, and Server3. You create a server grouping named ServerGroup1. Y'all discover the fault message shown in the post-obit exhibit. (Click the Showroom push.)

You need to ensure that Server2 can be managed remotely by using Server Manager. What should y'all do?
A. On DC1, run the Enable-PSSessionConfiguration cmdlet.
B. On Server2, run the Add-Reckoner cmdlet.
C. On Server2/ modify the membership of the Remote Management Users group.
D. From Active Directory Users and Computers, add together a computer account named Server2, and and so restart Server2.
Answer: C
Caption:
This is a security issue. To be able to access Server2 remotely through Server Manager the user need to be a member of the Remote Management Users group.
Incorrect:
Not A: the Enable-PSSessionConfiguration.This is an avant-garde cmdlet that is designed to exist used by system administrators to manage customized session configurations for their users.
Reference: Enable-ServerManagerStandardUserRemoting
QUESTION 189
Yous have a server named Server1 that runs Windows Server 2012 R2. Server1 has the Hyper-V server role installed. An iSCSI SAN is available on the network. Server1 hosts iv virtual machines named VM1, VM2, VM3, and VM4. You create a LUN on the SAN. You lot need to provide VM1 with access to the LUN. The solution must forbid other virtual machines from accessing the LUN. What should y'all configure?
A. A fixed-size VHDX
B. A fixed-size VHD
C. A dynamically expanding VHD
D. A dynamically expanding VHDX
E. A pass-through deejay
Answer: E
Explanation:
Y'all can use physical disks that are directly attached to a virtual auto as a storage option on the management operating system. This allows virtual machines to access storage that is mapped directly to the server running Hyper-V without starting time configuring the volume. The storage tin can be either a concrete disk which isinternal to the server, or a SAN logical unit of measurement number (LUN) that is mapped to the server (a LUN is a logical reference to a portion of a storage subsystem). The virtual machine must have exclusive admission to the storage, so the storage must be set in an Offline state in Disk Direction. The storage is not limited insize, and then it can exist a multitera byte LUN. When using physical disks that are directly attached to a virtual auto, y'all should exist enlightened of the following:
– This blazon of disk cannot exist dynamically expanded.
– You cannot use differencing disks with them.
– Yous cannot take virtual hd snapshots.
Note:
If you are installing an operating organisation on the physical disk and it is in an Online land before the virtual motorcar is started, the virtual auto will fail to start. You must store the virtual auto configuration file inan alternating location considering the concrete disk is used past the operating system installation. For example,locate the configuration file on another internal drive on the server running Hyper-Five.
http://technet.microsoft.com/en-united states/library/ee344823%28v=ws.ten%29.aspx
http://blogs.technet.com/b/askcore/archive/2008/10/24/configuring-pass-through-disks-inhyper-v.aspx
QUESTION 190
Your network contains an Active Directory domain named contoso.com. The domain contains a print server named Server1 that runs Windows Server 2012 R2. Server1 contains a local group named Group1. You share a printer named Printer1 on Server1. You need to configure Printer1 to meet the following requirements:
– Ensure that the members of Group1, the Server Operators group, the Administrators group, and the Impress Operators group can ship impress jobs to Printer1.
– Prevent other users from sending print jobs to Printer1.
Which 2 actions should you perform? (Each correct reply presents part of the solution. Cull 2.)
A. Assign the Print permission to the Server Operators group.
B. Remove the permissions for the Creator Possessor group.
C. Remove the permissions for the Everyone group.
D. Assign the Print permission to Group1.
East. Assign the Print permission to the Administrators group.
Reply: CD
Explanation:
C: To prevent other users from sending print jobs to Printer1.
D: To enable Group1 to send impress jobs.
Annotation: The Server Operators group, the Administrators group, and the Print Operators group are all built-in and already accept permissions to send impress jobs.
QUESTION 191
You have a new server named Server1 that runs Windows Server 2012 R2. Server1 has two dual-core processors and 32 GB of RAM. Yous install the Hyper-5 server role on Server1. You create ii virtual machines on Server1 that each accept eight GB of retention. You demand to minimize the amount of fourth dimension it takes for both virtual machines to access retention. What should you configure on each virtual auto?
A. Resource command
B. Dynamic Memory
C. NUMA topology
D. Retentivity weight
Answer: C
Explanation:
Windows Server 2012 introduced back up for projecting a virtual NUMA topology into Hyper-Five virtual machines. This capability can help improve the operation of workloads running on virtual machines that are configured with large amounts of memory.
QUESTION 192
Hotspot Question
Your network contains an Active Directory domain named contoso.com. Domain controllers run either Windows Server 2008 R2 or Windows Server 2012 R2. All client computers run Windows eight. All computer accounts are located in an organizational unit (OU) named OU1. You create a Group Policy Object (GPO) that contains several AppLocker rules. You link the GPO to OU1. You need to ensure that the AppLocker rules apply to all of the client computers. What should you lot configure in the GPO? To answer, select the appropriate service in the answer area.

Answer:

QUESTION 193
Hotspot Question
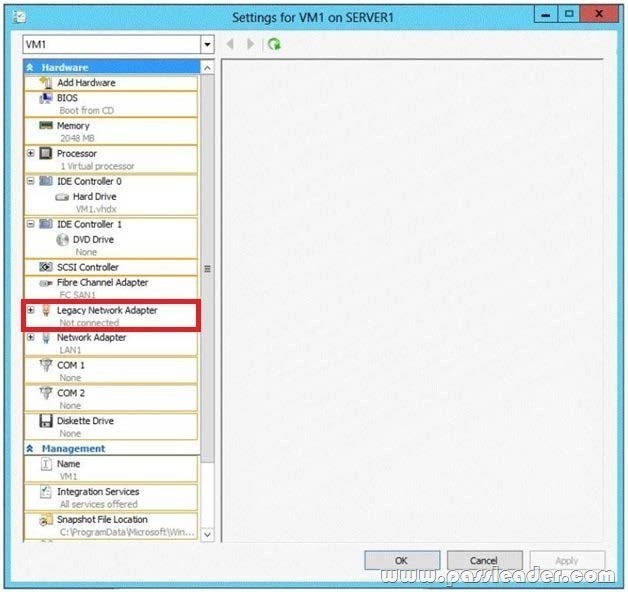
Your network contains an Agile Directory domain named contoso.com. Technicians use Windows Deployment Services (WDS) to deploy Windows Server 2012 R2. The network contains a server named Server1 that runs Windows Server 2012 R2. Server1 has the Hyper-5 server role installed. Y'all need to ensure that y'all can utilise WDS to deploy Windows Server 2012 R2 to a virtual machine named VM1. Which settings should you configure? To reply, select the appropriate settings in the answer expanse.

Respond:
QUESTION 194
Hotspot Question
Your network contains an Active Directory domain named contoso.com. The domain contains a fellow member server named Hyperv1 and a domain controller named DC1. Hyperv1 has the Hyper-V server part installed. DC1 is a virtual machine on Hyperv1. Users report that the time on their customer computer is incorrect. Yous log on to DC1 and verify that the time services are configured correctly. You demand to prevent time conflicts between the time provided past DC1 and other potential fourth dimension sources. What should y'all configure? To answer, select the appropriate object in the answer area.
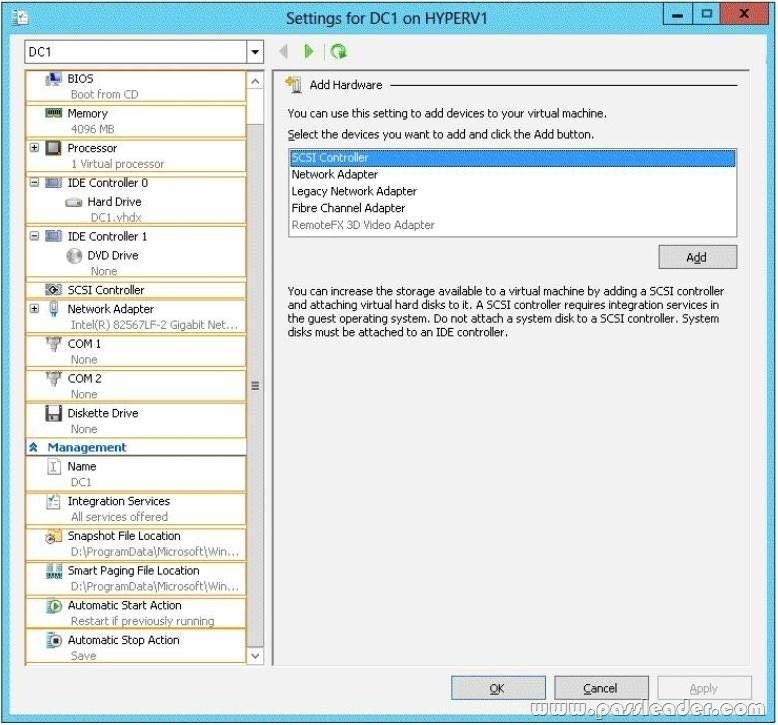
Answer:
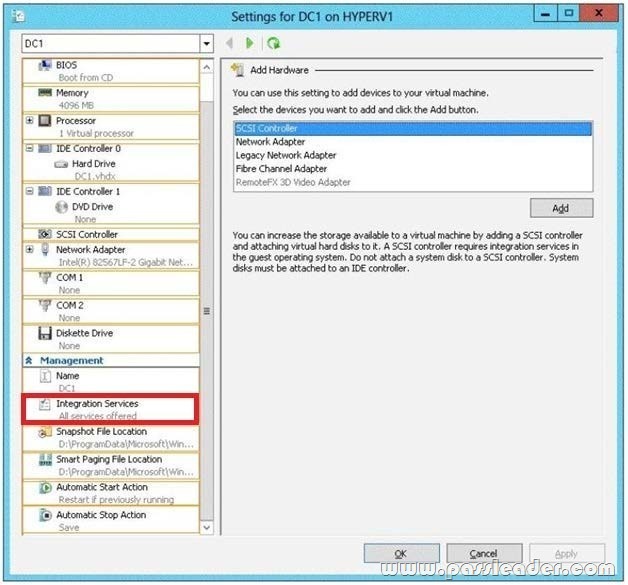
QUESTION 195
Yous perform a Server Cadre Installation of Windows Server 2012 R2 on a server named Server1. You need to add together a graphical user interface (GUI) to Server1. Which tool should you use?
A. the dism.exe command
B. the Add-WindowsFeature cmdlet
C. the imagex.exe control
D. the setup.exe command
E. the ocsetup.exe command
F. the Add-WindowsPackage cmdlet
Yard. the Install-Module cmdlet
H. the Install-RoleService cmdlet
Reply: AB
Caption:
Add-WindowsFeature -The Add-WindowsFeature cmdlet allows you to install specified roles, part services, and features on a computer that is running Windows Server 2008 R2.
Install-WindowsFeature -Installs ane or more Windows Server roles, role services, or features on either the local or a specified remote server that is running Windows Server 2012 R2. This cmdlet is equivalent to and replaces Add-WindowsFeature, the cmdlet that was used to install roles, role services, and features in Windows Server 2008 R2.
http://technet.microsoft.com/en-us/library/hh824822.aspx
http://technet.microsoft.com/en-us/library/dd744582(v=ws.10).aspx
http://technet.microsoft.com/en-us/library/jj205467(v=wps.620).aspx
QUESTION 196
You have a server named Server1 that runs Windows Server 2012 R2. Server1 has the Hyper-V server part installed. You lot need to configure storage for a virtual machine to meet the following requirements:
– Support upward to 3 TB of information on a single hard deejay.
– Allocate disk space as needed.
– Use a portable storage format.
What should you configure?
A. A laissez passer-through deejay
B. A fixed-size VHD
C. A dynamically expanding VHD
D. A fixed-size VHDX
E. A dynamically expanding VHDX
Answer: E
Explanation:
http://technet.microsoft.com/en-united states/library/hh831446.aspx
Support for virtual hard disk drive storage chapters of upwards to 64TB. VHD max is 2TB.
QUESTION 197
Your network contains an Agile Directory domain named contoso.com. All user accounts are in an organizational unit (OU) named Employees. You create a Group Policy Object (GPO) named GP1. You link GP1 to the Employees OU. Y'all need to ensure that GP1 does not utilize to the members of a grouping named Managers. What should you lot configure?
A. The Security settings of Employees
B. The WMI filter for GP1
C. The Block Inheritance option for Employees
D. The Security settings of GP1
Reply: D
Caption:
A. Wrong Group.
B. Windows Management Instrumentation (WMI) filters allow you to dynamically determine the telescopic of Grouping Policy Objects (GPOs) based on attributes of the target estimator.
C. Blocking inheritance prevents Group Policy Objects (GPOs) that are linked to higher sites, domains, or organizational units from existence automatically inherited by the child-level.
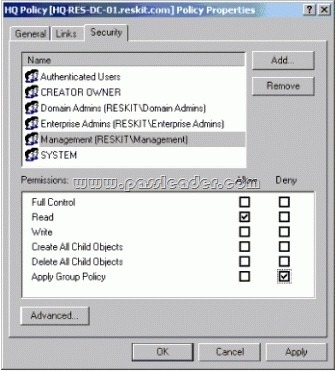
D. Set Managers to – Members of this security grouping are exempt from this Group Policy Object.
Note: Security settings. Yous use the Security Settings extension to gear up security options for computers and users within the scope of a Group Policy Object. Y'all tin can define local computer, domain, and network security settings. Figure belows shows an example of the security settings that allow everyone to be afflicted by this GPO except the members of the Management grouping, who were explicitly denied permission to the GPO by setting the Apply Group Policy ACE to Deny. Notation that if a fellow member of the Direction group were also a member of a group that had an explicit Allow setting for the Utilise Grouping Policy ACE, the Deny would take precedence and the GPO would not impact the user.

http://technet.microsoft.com/en-us/library/bb742376.aspx
http://technet.microsoft.com/en-us/library/cc786636(WS.10).aspx
http://technet.microsoft.com/en-us/library/cc731076.aspx
http://technet.microsoft.com/en-us/library/cc779036(v=ws.10).aspx
QUESTION 198
You lot have a virtual machine named VM1. You install Windows Server 2012 R2 on VM1. You lot plan to utilise VM1 as an image that will exist distributed to sales users to demonstrate the features of a custom awarding. The custom application only requires the Web Server (IIS) server function to be installed. You demand to ensure that the VHD file for VM1 just contains the required Windows Server 2012 R2 source files. Which tool should you use?
A. dism.exe
B. ocsetup.exe
C. imagex.exe
D. servermanagercmd.exe
Answer: A
Explanation:
http://technet.microsoft.com/en-us/magazine/dd490958.aspx
You tin can use DISM to:
– Add together, remove, and enumerate packages and drivers.
– Enable or disable Windows features.
– Use changes based on the offline servicing section of an unattend.xml respond file.
– Configure international settings.
– Upgrade a Windows epitome to a different edition.
– Prepare a Windows PE paradigm.
– Accept advantage of better logging.
– Service down-level operating systems like Windows Vista with SP1 and Windows Server 2008.
– Service all platforms (32-bit, 64-bit, and Itanium).
– Service a 32-chip image from a 64-bit host and service a 64-bit epitome from a 32-bit host.
– Make utilize of old Package Managing director scripts.
QUESTION 199
Your network contains an Agile Directory domain named contoso.com. The domain contains a server named Server1. Server1 runs Windows Server 2012 R2 and has the Hyper-V server role installed. On Server1, you create and start a virtual machine named VM1. VM1 is configured as shown in the following table.
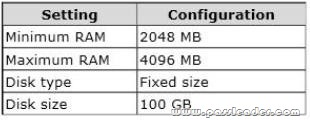
You plan to create a snapshot of VM1. You need to recommend a solution to minimize the amount of disk space used for the snapshot of VM1. What should yous practice earlier you lot create the snapshot?
A. Run the Cease-VM cmdlet.
B. Run the Catechumen-VHD cmdlet.
C. Decrease the Maximum RAM
D. Decrease the Minimum RAM.
Reply: A
Explanation:
What are virtual machine snapshots?
Virtual car snapshots capture the country, data, and hardware configuration of a running virtual auto.
What are snapshots used for?
Snapshots provide a fast and like shooting fish in a barrel style to revert the virtual machine to a previous state. For this reason, virtual machine snapshots are intended mainly for use in development and test environments. Having an easy way to revert a virtual machine can be very useful if yous need to recreate a specific country or condition and then that you tin can troubleshoot a problem. At that place are certain circumstances in which it may brand sense to use snapshots in a production environs. For example, you can use snapshots to provide a way to revert a potentially risky operation in a production environment, such every bit applying an update to the software running in the virtual machine.
How are snapshots stored?
Snapshot data files are stored equally .avhd files. Taking multiple snapshots can apace swallow storage space. In the first release version of Hyper-V (KB950050) and in Hyper-V in Windows Server 2008 Service Pack 2, snapshot, snapshot information files unremarkably are located in the same folder as the virtual machine by default. In Hyper-V in Windows Server 2008 R2, the files normally are located in the same folder as the virtual hard deejay. The following exceptions affect the location of the snapshot data files: If the virtual machine was imported with snapshots, they are stored in their own folder. If the virtual machine has no snapshots and you configure the virtual automobile snapshot setting, all snapshots you have afterwards will be stored in the folder you specify.
http://technet.microsoft.com/pt-pt/library/dd560637%28v=ws.10%29.aspx
QUESTION 200
Your network contains an Active Directory domain named contoso.com. The domain contains a file server named Server1 that runs Windows Server 2012 R2. Server1 contains a shared folder named Share1. Share1 contains the home folder of each user. All users have the necessary permissions to access just their home binder. The users report that when they admission Share1, they can see the home folders of all the users. Y'all need to ensure that the users see only their home folder when they access Share1. What should you do from Server1?
A. From Windows Explorer, alter the properties of the volume that contains Share1.
B. From Server Manager, modify the properties of the book that contains Share1.
C. From Server Director, modify the properties of Share1.
D. From Windows Explorer, alter the properties of Share1.
Answer: C
Caption:
http://technet.microsoft.com/en-us/library/cc784710(5=ws.10).aspx
Admission based enumeration needs to exist enabled:

Get the newest PassLeader 70-410 VCE dumps here: http://www.passleader.com/seventy-410.html (512 Q&As Dumps –> 528 Q&Equally Dumps)
And, DOWNLOAD the newest PassLeader seventy-410 PDF dumps from Cloud Storage for free: https://drive.google.com/open?id=0B-ob6L_QjGLpfnJzOE1fWnlJOWVtaE93SnJNT3gtaTNYYnVpZkw5THBSMWRKbFlfaXh1azg
DOWNLOAD HERE
Posted by: baldwinlabody.blogspot.com
Post a Comment